
SpringBoot结合jasypt进行配置文件加解密的方法步骤
16人参与 • 2026-09-16 • Java
一、前言
随着当前安全 局势愈发严峻,各行业安全要求越来越高,本文重点介绍springboot结合jasypt进行数据库等配置文件进行加解密的方法。
二、基础使用
2.1 引入依赖
<dependency>
		<groupid>com.github.ulisesbocchio</groupid>
		<artifactid>jasypt-spring-boot-starter</artifactid>
		<version>3.0.5</version>
	</dependency>
2.2 增加配置
jasypt:
  encryptor:
    algorithm: pbewithmd5anddes  #指定解密算法
    password: wno704 #加密的密钥,自定义即可,必填项.
    iv-generator-classname: org.jasypt.iv.noivgenerator
    property: # 自定义的前后缀标记,格式为enc(加密结果),此处我们修改为 wno704-密文-end
      prefix: wno704-
      suffix: -end
2.3 获取加密密文
在本地maven仓库中找到 org/jasypt/jasypt/1.9.3 目录(根据版本不同,目录不同),然后执行下面命令:
加密
java -cp jasypt-1.9.3.jar org.jasypt.intf.cli.jasyptpbestringencryptioncli password=${password} algorithm=${algorithm} input=${input}解密
java -cp jasypt-1.9.3.jar org.jasypt.intf.cli.jasyptpbestringdecryptioncli password=${password} algorithm=${algorithm} input=${input}password: 加密的salt,解密时还需要它,项目自定义
algorithm: 加密的类型,默认 pbewithmd5anddes
input: 待加密的明文
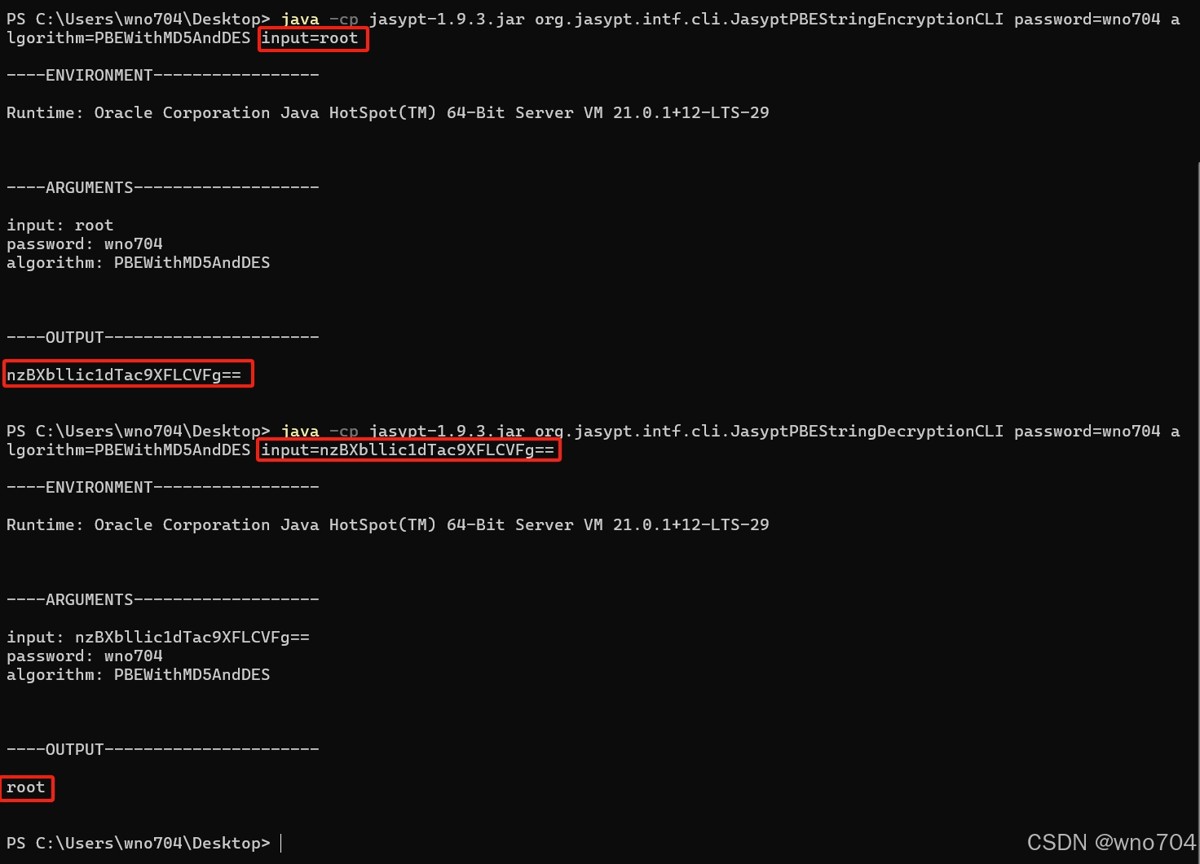
执行结果中 output 下方的内容时明文对应的密文或者明文,如果是加密过程多次执行同一个命令 output 输出的内容不同,但不影响。
实际执行如下:
三、进阶使用
加解密工具jasyptutil.java
package com.wno704.system.util;

import org.jasypt.encryption.pbe.standardpbestringencryptor;
import org.jasypt.encryption.pbe.config.environmentstringpbeconfig;

/**
 * @calssname jasyptutil
 * @description todo
 * @author wno704
 * @date 2024/10/14 下午3:22
 * @version 1.0
 */
public class jasyptutil {

    /**
     * 加密
     *
     * @param plaintext 明文
     * @return
     */
    public static string encrypt(string plaintext) {
        standardpbestringencryptor encryptor = new standardpbestringencryptor();
        environmentstringpbeconfig config = new environmentstringpbeconfig();
        // 指定算法
        config.setalgorithm("pbewithmd5anddes");
        // 指定秘钥,和yml配置文件中保持一致
        config.setpassword("wno704");
        encryptor.setconfig(config);
        // 生成加密数据
        return encryptor.encrypt(plaintext);
    }

    /*
     * @description: 加密
     * @param: [algorithm, password, plaintext]
     * @return: java.lang.string
     * @author: wno704
     * @date: 2024/10/14
     */
    public static string encrypt(string algorithm,string password,string plaintext) {
        standardpbestringencryptor encryptor = new standardpbestringencryptor();
        environmentstringpbeconfig config = new environmentstringpbeconfig();
        // 指定算法
        config.setalgorithm(algorithm);
        // 指定秘钥,和yml配置文件中保持一致
        config.setpassword(password);
        encryptor.setconfig(config);
        // 生成加密数据
        return encryptor.encrypt(plaintext);
    }

    /**
     * 解密
     *
     * @param data 加密后数据
     * @return
     */
    public static string decrypt(string data) {
        standardpbestringencryptor encryptor = new standardpbestringencryptor();
        environmentstringpbeconfig config = new environmentstringpbeconfig();
        config.setalgorithm("pbewithmd5anddes");
        config.setpassword("wno704");
        encryptor.setconfig(config);
        // 解密数据
        return encryptor.decrypt(data);
    }

    /**
     * 解密
     *
     * @param data 加密后数据
     * @return
     */
    public static string decrypt(string algorithm,string password,string data) {
        standardpbestringencryptor encryptor = new standardpbestringencryptor();
        environmentstringpbeconfig config = new environmentstringpbeconfig();
        config.setalgorithm(algorithm);
        config.setpassword(password);
        encryptor.setconfig(config);
        // 解密数据
        return encryptor.decrypt(data);
    }

    /*
     * @description: 字符串前后缀取消
     * @param: [prefix, suffix, str]
     * @return: java.lang.string
     * @author: wno704
     * @date: 2024/10/14
     */
    public static string dealstrfix(string prefix, string suffix, string str){
        string restr = str;
        if (str.indexof(prefix)==0){
            restr = str.replacefirst(prefix, "");
        }
        if (restr.lastindexof(suffix) == restr.length() - suffix.length()) {
            restr = restr.substring(0, restr.length() - suffix.length());
        }
        return restr;
    }

    /*
     * @description: 是否符合前后缀要求
     * @param: [prefix, suffix, str]
     * @return: java.lang.string
     * @author: wno704
     * @date: 2024/10/14
     */
    public static boolean iscontainfix(string prefix, string suffix, string str){
        string restr = str;
        if (str.indexof(prefix)==0){
            restr = str.replacefirst(prefix, "");
        }
        if (restr.lastindexof(suffix) == restr.length() - suffix.length()) {
            restr = restr.substring(0, restr.length() - suffix.length());
        }
        return restr.length()+prefix.length()+suffix.length() == str.length();
    }
}
工具使用
    @test
    public void testjasypt() throws exception {
        string oldstr = "19920503";
        string enstr = jasyptutil.encrypt(oldstr);
        system.out.println(enstr);
        system.out.println(jasyptutil.decrypt(enstr));

        enstr = jasyptutil.encrypt("pbewithmd5anddes","wno704",oldstr);
        system.out.println(enstr);
        system.out.println(jasyptutil.decrypt("pbewithmd5anddes","wno704", enstr));

        string destr = "wno7041-2hudacddwno704-v5wh-endfszktp5rfw==-end";
        string prefix = "wno704-";
        string suffix = "-end";

        system.out.println(jasyptutil.iscontainfix(prefix,suffix,destr));
        system.out.println(jasyptutil.dealstrfix(prefix,suffix,destr));
        system.out.println(jasyptutil.decrypt("pbewithmd5anddes","wno704", "jwkjxvnywwb51ftdwvkytx2ijqqeuwmy"));
    }
到此这篇关于springboot结合jasypt进行配置文件加解密的方法步骤的文章就介绍到这了,更多相关springboot jasypt配置文件加解密内容请搜索代码网以前的文章或继续浏览下面的相关文章希望大家以后多多支持代码网!
赞 (0)
您想发表意见!!点此发布评论


发表评论